Surveillance systems in 2026 and what buyers should evaluate before upgrading
a[data-rs-seo-link]{text-decoration:underline!important;color:#1a56db!important;cursor:pointer!important;}a[data-rs-seo-link]{text-decoration:underline!important;color:#1a56db!important;cursor:pointer!important;}
What surveillance systems now need to do
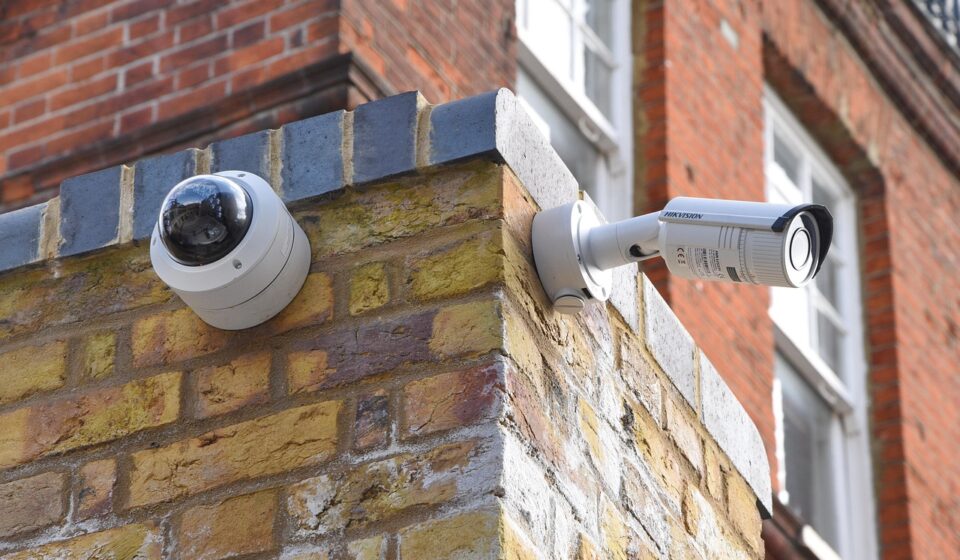
Surveillance systems in 2026 are no longer just groups of cameras connected to a recorder. They are networked security platforms that capture sensitive video, support investigations, trigger alerts, integrate with access control, and create cybersecurity and privacy obligations. An upgrade plan therefore has to look at image quality, storage, analytics, network design, interoperability, cyber hardening, retention rules, and human review as one system.
For facility owners, schools, warehouses, retail sites, offices, and multi-site operators, the practical question is not simply how many cameras to buy. It is whether the system can produce reliable evidence, shorten response time, protect data, and remain manageable over its expected service life. For broader coverage of surveillance systems, start with system architecture rather than camera specifications alone.
The shift from cameras to connected risk platforms
The security industry has been moving from device-centered surveillance toward software-led platforms. That shift is visible in three areas: artificial intelligence for event detection, cloud or hybrid video management, and tighter links between video, access control, alarms, and operational data. The Security Industry Association identified AI as a major 2026 security industry theme, while Genetec’s 2026 State of Physical Security Report placed AI alongside video surveillance and access control as a leading project priority. Omdia also reported that the global video surveillance market reached about $27 billion in 2025, with AI analytics and video surveillance as a service contributing to software growth.
Those figures do not mean every site needs facial recognition, real-time behavioral analytics, or a full cloud migration. They do show why buyers should stop judging surveillance systems only by resolution and camera count. A 4K camera that is difficult to patch, cannot export usable evidence, or depends on weak remote access may create more risk than value. By contrast, a modest camera layout with defined retention, strong account controls, reliable storage, and well-tuned alerts can be more useful than a large unmanaged deployment.
For buyers, the main implication is that surveillance now sits between physical security and information security. The camera, recorder, video management software, switch, mobile app, user account, cloud tenant, and evidence export workflow all form part of the same risk surface.
Core components of a modern surveillance system
Cameras and sensors
Camera choice still matters, but it should follow the security objective. A doorway may need face-level identification under changing light. A parking lot may need wide coverage, license plate capture, or low-light performance. A warehouse aisle may need object movement detection and a clear view of loading areas. The same camera specification can perform very differently depending on lens selection, mounting height, backlighting, compression settings, and scene motion.
Modern IP cameras often include edge analytics such as person detection, vehicle detection, line crossing, loitering alerts, or tamper detection. These functions can reduce noise compared with basic motion detection, but they are not perfect. Rain, reflections, insects, shadows, forklifts, and seasonal lighting changes can still generate false alerts. Buyers should ask how alerts are tuned, where analytic processing happens, and whether analytics can be disabled or limited in sensitive areas.
Video management and recording
The video management layer determines how users view live feeds, search recordings, export evidence, manage permissions, and integrate video with other systems. Storage may be local through an NVR, centralized through servers, cloud-based, or hybrid. Each model has trade-offs. Local recording can offer predictable control and bandwidth efficiency, but it may be harder to manage across many sites. Cloud-managed platforms can simplify updates and remote access, but they require careful review of data location, subscription costs, bandwidth, export limits, and provider security controls.
Retention should be designed before storage is purchased. A site retaining 20 cameras for 14 days has a different storage requirement from a regulated site retaining 100 cameras for 90 days. Resolution, frame rate, codec, scene complexity, and recording mode all affect the result. A practical planning formula is simple: define camera count, average bitrate, recording hours per day, retention days, and redundancy needs. Then add headroom for growth and incident holds.
Network, power, and identity
PoE switching, VLAN segmentation, firewall rules, time synchronization, and identity management are not secondary details. They determine whether the system stays stable and secure. Cameras should not be placed on the same flat network as business workstations without a deliberate reason. Remote viewing should avoid open inbound exposure wherever possible and should rely on strong authentication, least-privilege accounts, and logging.
Accurate time is also critical. If video timestamps are inconsistent across cameras, access control logs, alarm events, and incident reports, the system can lose evidentiary value. Network time protocol configuration, recorder health monitoring, and storage failure alerts should be part of commissioning rather than optional maintenance items.
Cybersecurity should be part of the specification
Connected surveillance devices are IoT devices, and public guidance has become clearer about what responsible security should include. NIST’s IoT cybersecurity publications, including the NISTIR 8259 series and SP 800-213, emphasize capabilities such as device identification, secure configuration, data protection, logical access control, software updates, and cybersecurity state awareness. NIST released Cybersecurity Framework 2.0 on February 26, 2024, adding a Govern function to Identify, Protect, Detect, Respond, and Recover, which is especially relevant when security systems collect sensitive operational data.
For surveillance systems, this translates into practical procurement requirements. Buyers should ask whether devices support unique credentials, role-based access, encrypted management sessions, signed firmware, vulnerability reporting, update documentation, audit logs, and secure reset processes. CISA’s secure-by-design guidance has repeatedly criticized default passwords and unsafe default configurations across connected products. A camera that requires shared administrator accounts or cannot receive timely firmware updates should be treated as a risk, even if its image quality is strong.
Cybersecurity review should also cover the vendor and integrator relationship. Who has remote access? Is access time-limited and logged? Are support accounts disabled when a project ends? Are cloud administrators protected with multi-factor authentication? Can the organization export logs during an incident? In many upgrades, these questions matter more than a small difference in camera resolution.
Compliance and supply chain issues require early screening
For U.S. public sector work, federally funded projects, critical infrastructure, and contractors serving government customers, equipment eligibility can be a deciding factor. Section 889 of the 2019 National Defense Authorization Act and related Federal Acquisition Regulation language restrict certain telecommunications and video surveillance equipment or services associated with named manufacturers and affiliates in specified federal contexts. The FCC Covered List and federal grant rules such as 2 CFR 200.216 can also affect procurement decisions. Private buyers that do not work with federal money may face different requirements, but many still screen supply chains to reduce national security, compliance, and resale risk.
The key point is not to rely on a marketing phrase alone. Terms such as NDAA compliant are common in the market, but buyers should request model-level documentation, manufacturer declarations, bill-of-materials clarity when available, and confirmation from the party responsible for the project. Rebranded or white-label equipment can complicate review because the visible logo may not tell the full manufacturing story.
Interoperability is another form of supply chain protection. ONVIF Profile T, for example, is designed for IP-based video systems and supports features such as H.264 and H.265 video, motion and tampering events, metadata streaming, and related advanced streaming functions. ONVIF support does not guarantee that every feature works across every recorder, client, and camera combination, but profile-level compatibility can reduce lock-in compared with proprietary-only designs. See also: Access Control.
Privacy, retention, and human review need written rules
Surveillance can improve safety, but it also collects information about employees, visitors, customers, residents, vendors, and bystanders. That makes privacy governance a core design issue. The FTC’s actions involving Ring in 2023 and Verkada in 2024 show that regulators pay attention to both unauthorized access to camera feeds and claims about security practices. The lesson for organizations is direct: do not collect more than necessary, do not give more people access than necessary, and do not keep footage longer than necessary without a defined reason.
Practical privacy controls begin with camera placement. Avoid recording private spaces such as restrooms, changing areas, wellness rooms, and areas where people reasonably expect privacy. For workplaces, schools, healthcare-adjacent facilities, residential communities, and public-facing spaces, state and local rules may add notice, consent, labor, biometric, or audio-recording requirements. Audio recording is especially sensitive because consent laws vary by state.
Retention should be tied to business need. Common reasons include incident investigation, insurance review, workplace safety, regulatory obligations, and law enforcement requests. A written retention schedule should define normal deletion periods, legal hold procedures, export approval, chain-of-custody handling, and who can review footage. Without these rules, surveillance systems can drift into overcollection and inconsistent use.
A practical evaluation framework for upgrades
A strong request for proposal or internal project plan should compare systems across operational, cyber, legal, and lifecycle factors. The table below gives buyers a concise way to organize that review.
| Evaluation area | What to verify | Why it matters |
|---|---|---|
| Security objective | Coverage goals, identification needs, response workflow, and evidence requirements | Prevents buying cameras that do not solve the actual risk |
| Image performance | Lens, field of view, low-light behavior, frame rate, dynamic range, and mounting plan | Determines whether footage is usable when an incident occurs |
| Storage design | Bitrate assumptions, retention days, redundancy, export speed, and incident holds | Controls cost and preserves evidence availability |
| Cybersecurity | Unique credentials, MFA where available, patch process, encryption, logs, and segmentation | Reduces the chance that cameras become an entry point or privacy failure |
| Interoperability | ONVIF profile support, API access, VMS compatibility, and export formats | Limits vendor lock-in and supports future upgrades |
| Compliance | Federal procurement restrictions, grant conditions, privacy rules, and audio or biometric limits | Helps avoid costly replacement or policy violations |
| Operations | User roles, training, health monitoring, alert tuning, and maintenance responsibility | Keeps the system useful after installation |
This framework also helps separate source facts from vendor claims. A vendor can describe a product feature, but the buyer still needs to confirm how that feature works in the actual environment, including the site’s lighting, bandwidth, staffing, and policy constraints.
Upgrade roadmap for existing sites
Many organizations do not need a full replacement on day one. A phased plan usually creates less disruption and better budget control. Start with an inventory of cameras, recorders, switches, firmware versions, user accounts, open ports, warranty status, and known blind spots. Then map the system against current risks such as theft patterns, workplace incidents, visitor flow, perimeter exposure, after-hours access, and investigation pain points.
Next, fix the highest-risk basics. Remove unused accounts, change shared passwords, document administrator access, close unnecessary external exposure, test backups and exports, and confirm retention settings. Replace failing storage and unsupported devices before adding advanced analytics. If the system is used for compliance-sensitive work, screen equipment and vendors before purchasing replacements.
After the foundation is stable, evaluate analytics and cloud services through a pilot. Test false alerts, search speed, mobile access, bandwidth, evidence export, and user permissions with real scenes. A pilot should include security staff, IT, facilities, legal or compliance stakeholders, and the people who will respond to alerts. Surveillance systems fail most often when they are designed around a specification sheet rather than the daily workflow of the site.
Frequently asked questions
Are cloud surveillance systems safer than local NVR systems?
Neither model is automatically safer. Cloud systems can simplify updates, remote access, and multi-site management, but they introduce provider, bandwidth, account, and data-location considerations. Local NVR systems can provide more direct control, but they still need patching, network segmentation, strong passwords, and backup planning. The safer choice is the one with better governance, configuration, monitoring, and support for the site’s risk profile.
How long should surveillance footage be kept?
There is no single retention period that fits every site. Many organizations choose a period based on incident discovery time, insurance needs, legal obligations, storage cost, and privacy risk. A useful policy defines normal retention, longer holds for incidents, deletion procedures, and who may approve exports. Keeping footage indefinitely without a defined purpose increases privacy and management risk.
Is AI video analytics worth adding?
AI analytics can be valuable when they reduce false alarms, speed investigations, or detect events that staff would otherwise miss. They should be tested in the actual scene before broad deployment. Buyers should also review privacy implications, alert accuracy, configuration effort, and whether analytics run on the camera, recorder, server, or cloud platform.
What is the biggest mistake when upgrading surveillance systems?
The biggest mistake is treating the project as a camera purchase instead of a system design. Image quality matters, but so do storage, network security, user permissions, retention rules, interoperability, compliance screening, and response procedures. A smaller well-managed system can outperform a larger system that lacks governance.
Do small businesses need the same cybersecurity controls as large facilities?
Small businesses may not need enterprise complexity, but they still need the basics: unique accounts, strong passwords, multi-factor authentication where available, firmware updates, secure remote access, limited user permissions, and a documented retention policy. These controls are especially important because small sites often rely on mobile apps and cloud access for daily monitoring.